Security & DevSecOps
Build it secure, keep it running
Sound familiar?
The problems we are usually called in to fix
- Problem 01
Security bolted on at the end
Penetration tests a week before launch find problems that are expensive to fix so late.
- Problem 02
Too many people with too much access
Shared passwords and broad permissions turn one compromised account into a full breach.
- Problem 03
Unclear data-protection obligations
Personal and financial data is collected without clear rules for consent, retention and access.
- Problem 04
No plan for the bad day
Backups are untested, alerts are missing and nobody is sure who does what during an incident.
What we deliver
What we build and run for you
Security-first architecture, privacy controls, hardened delivery pipelines and reliability engineering for systems that handle sensitive data.
Threat modelling & secure design
Identify how a system could be attacked and design the controls in from the start.
Zero-trust access
Short-lived tokens, OAuth2, multi-factor authentication and least-privilege roles for people and services.
Encryption & data masking
Encryption at rest and in transit, plus masking and anonymisation of personal data in analytics and AI.
Secure CI/CD
Automated tests and static security analysis that stop vulnerable code before it reaches production.
Monitoring & incident readiness
Alerting, tested backups and clear runbooks so incidents are caught early and handled calmly.
Privacy & governance
Data inventories, access policies and controls that support your data-protection obligations.
How it works
A clear path from idea to production
Working software every two weeks, demonstrated to you, with security and documentation built in from the first sprint.
- 01
Assess
Review architecture, access, code and infrastructure against common attack paths and your obligations.
- 02
Prioritise
A clear, ranked list of risks with practical fixes, not a 200-page report nobody reads.
- 03
Harden
Implement the controls: access, encryption, secrets management, pipeline checks and logging.
- 04
Verify
Test the controls, rehearse recovery and confirm that alerts reach the right people.
- 05
Sustain
Ongoing monitoring, patching and periodic reviews as your systems and threats change.
Use cases by industry
Where Security & DevSecOps pays off
Related work
Proof, not promises
 Banking
AI fraud & anti-money-laundering detection
Machine learning that scores transactions for fraud and money-laundering risk and flags suspicious activity with actionable intelligence.
- Python
- Django
- FastAPI
 Banking
AI loan approval & amount recommendation API
Production-ready CatBoost and NLP models that predict loan approvals and recommend suitable amounts in real time.
- Python
- FastAPI
- CatBoost
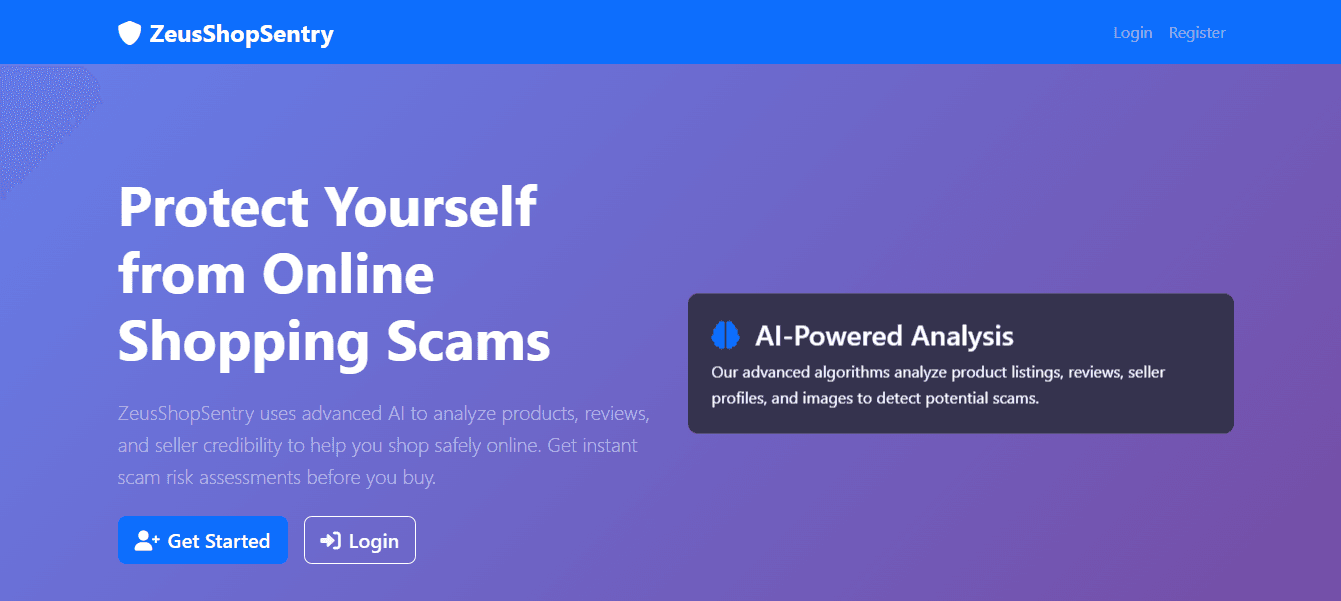 E-commerce
ZeusShopSentry
Detects online shopping scams by analysing product links, seller credibility and review patterns, then generates a trust report before you buy.
- Python
- Flask
- Fine-tuned LLMs
Tools and technologies behind our Security & DevSecOps work
- OAuth2
- JWT
- MFA
- AES-256 at rest
- TLS 1.3
- Docker
- CI/CD with SAST
- Secrets management
- Centralised logging
- Automated backups
FAQ
Security & DevSecOps questions, answered
Can you review a system you did not build?
Yes. We assess existing applications and infrastructure, then deliver a prioritised list of practical fixes and help implement them.
Do you help with data-protection compliance?
We implement the technical controls that support compliance, such as access control, encryption, retention and audit logs, and work alongside your legal advisers on policy.
How do you keep AI projects secure?
Sensitive fields are masked or anonymised before modelling, models can run on your own infrastructure, and every API is authenticated and logged.
What happens if something goes wrong after launch?
Monitoring and alerting are part of every delivery, and support agreements define response times by severity so critical issues get immediate attention.
Free assessment
Have a process that’s slow, manual or risky? Let’s engineer a smarter one.
An engineer, not a salesperson, will reply within one business day. The first assessment is free and there is no obligation.